Tool · Open source
bookmark-path-finder
Finds hidden paths and API routes on any page.
Cyber & Product Security EngineerCo‑Founder at Raqyan
I build secure products and break them before attackers do.
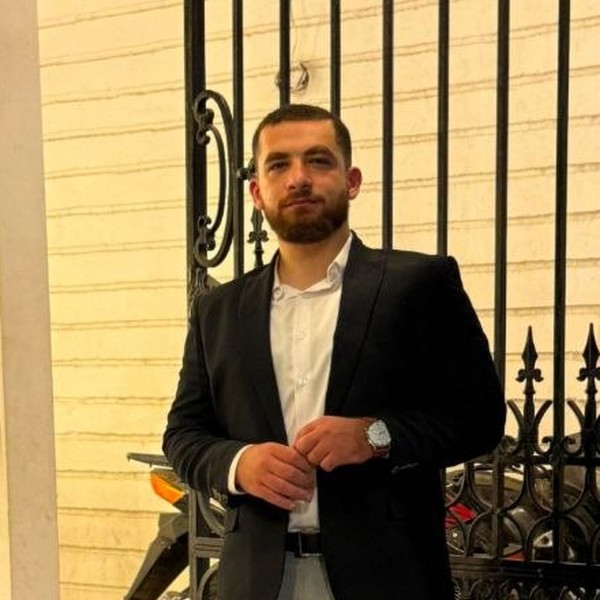
I make sure software is built, shipped, and tested so attackers can't break it.
Present
Raqyan Co-founder
Running delivery from code to production, with security built in.
Feb 2025 – Present
GCC Part-time
Testing client apps like an attacker, then reporting the fixes.
2023 – Present
HackerOne Part-time
Finding flaws in live products through bug bounty programs.
Jun 2025 – Aug 2025
Robusta Technology Group (RTG) Full-time
Helping product teams ship without security holes.
Oct 2023 – Jan 2024
Cybrany Part-time
Simulating attacks and researching new vulnerabilities.
Computer Science & Engineering
Faculty of Electronic Engineering, Menoufia University
Cyber Security Core Member, IEEE Menoufia University Student Branch
Arts Committee Member, FEE Student Union
Client engagements

Attackers don't care how big you are. I look at your product the way they do, find what could cost you money or customers, and fix it before it becomes a crisis.
What's at stake
Exposed records cost you customers, legal trouble, and your reputation.
Attackers log in as your users and drain balances, points, or data.
Flaws in checkout, coupons, or limits become direct financial losses.
Every hour offline means lost sales and broken promises to customers.
One vulnerable library or vendor can become your breach.
Enterprise customers ask for proof. Without it, the deal stalls.
What you get
Fewer surprises
Risks found and fixed before attackers find them.
Clear decisions
Findings ranked by business impact, in plain language for your team and leadership.
Faster deals
Evidence that helps you pass customer security reviews.
Full confidentiality
NDA-friendly. Findings are shared only with you.
How it works
Understand your business
What you sell, what you store, and what would hurt most.
Map the attack surface
Apps, APIs, cloud, and the people and vendors around them.
Test like an attacker
Real attack paths against what matters, not a generic checklist.
Fix, verify, retest
Clear fixes with your developers, then proof they hold.
Not sure where you're exposed?
Tell me about your product and I'll point out where the real risks are.
I came to security from software development, so I read code, not just responses, and understand what the developer intended.
I work on both sides: shipping software and attacking it.
Automated security checks and secure defaults in the delivery pipeline.
Secure code review and testing alongside developers.
Web, API, and Android testing, with every finding verified and a clear fix.
Finding vulnerabilities in live systems and disclosing them responsibly.
Testing AI features for prompt injection, weak auth, and data exposure.
Security domains I cover
Finds hidden paths and API routes on any page.
Found and reported through coordinated disclosure.
Nothing here yet.
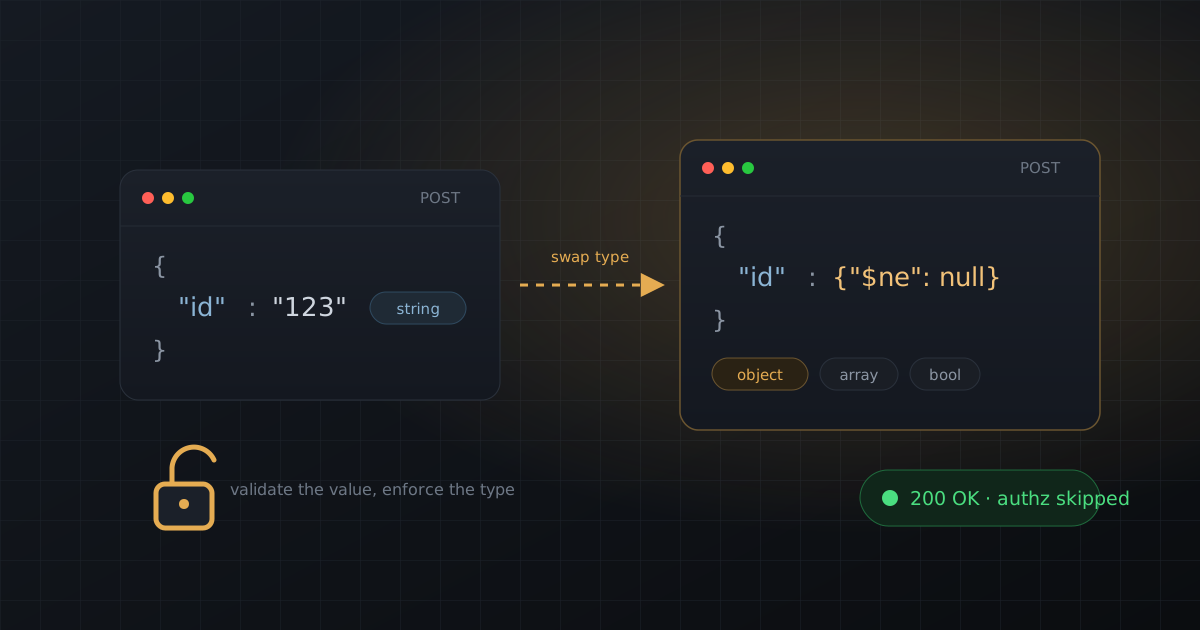
EngineeringSecuritySep 14, 2026 · 2 min read
Change a parameter's type, not just its value, to find authorization bugs.
Read article
SecurityDec 20, 2024 · 6 min read
From stored XSS in comments to file upload to remote code execution.
Read article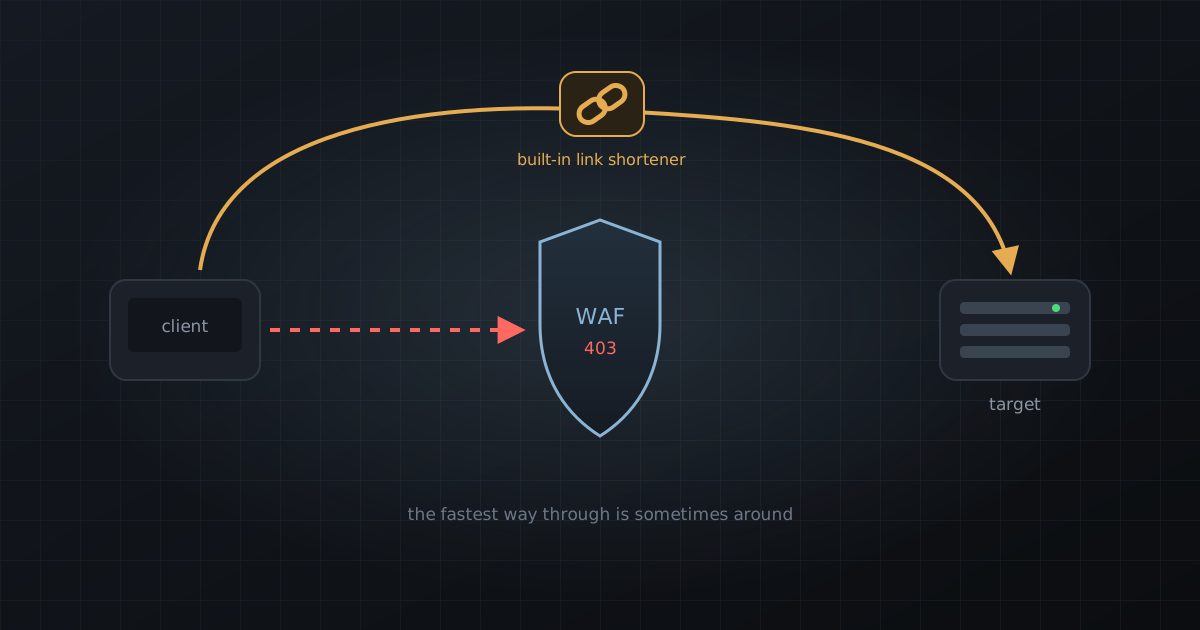
SecurityDec 5, 2024 · 3 min read
Getting past a WAF through the site's own link shortener.
Read article
eCPPT
Certified Professional Penetration Tester
eLearnSecurity / INE
eWPTX
Web Penetration Tester eXtreme
eLearnSecurity / INE
eMAPT
Mobile Application Penetration Tester
eLearnSecurity / INE
eAIS
AI Systems Security Specialist
eLearnSecurity / INE
Available for new engagements
Hiring, consulting, training, or a security project. I read every message.
Email me directly
imooaaz@gmail.com